A casino or sportsbook can look market-ready on the front end and still fail operationally behind the scenes. A game launch that does not update wallet balances correctly, a payment callback that is processed twice, or a provider outage that goes unnoticed can create immediate revenue, compliance, and customer-service pressure. That is why iGaming API development must be treated as core platform engineering, not a basic integration task.
For operators, platform owners, and market entrants, the objective is clear: connect the services required to run a regulated digital gaming business while retaining control over performance, data, commercial configuration, and future expansion. The API layer is where that control is either established or lost.
What iGaming API Development Must Deliver
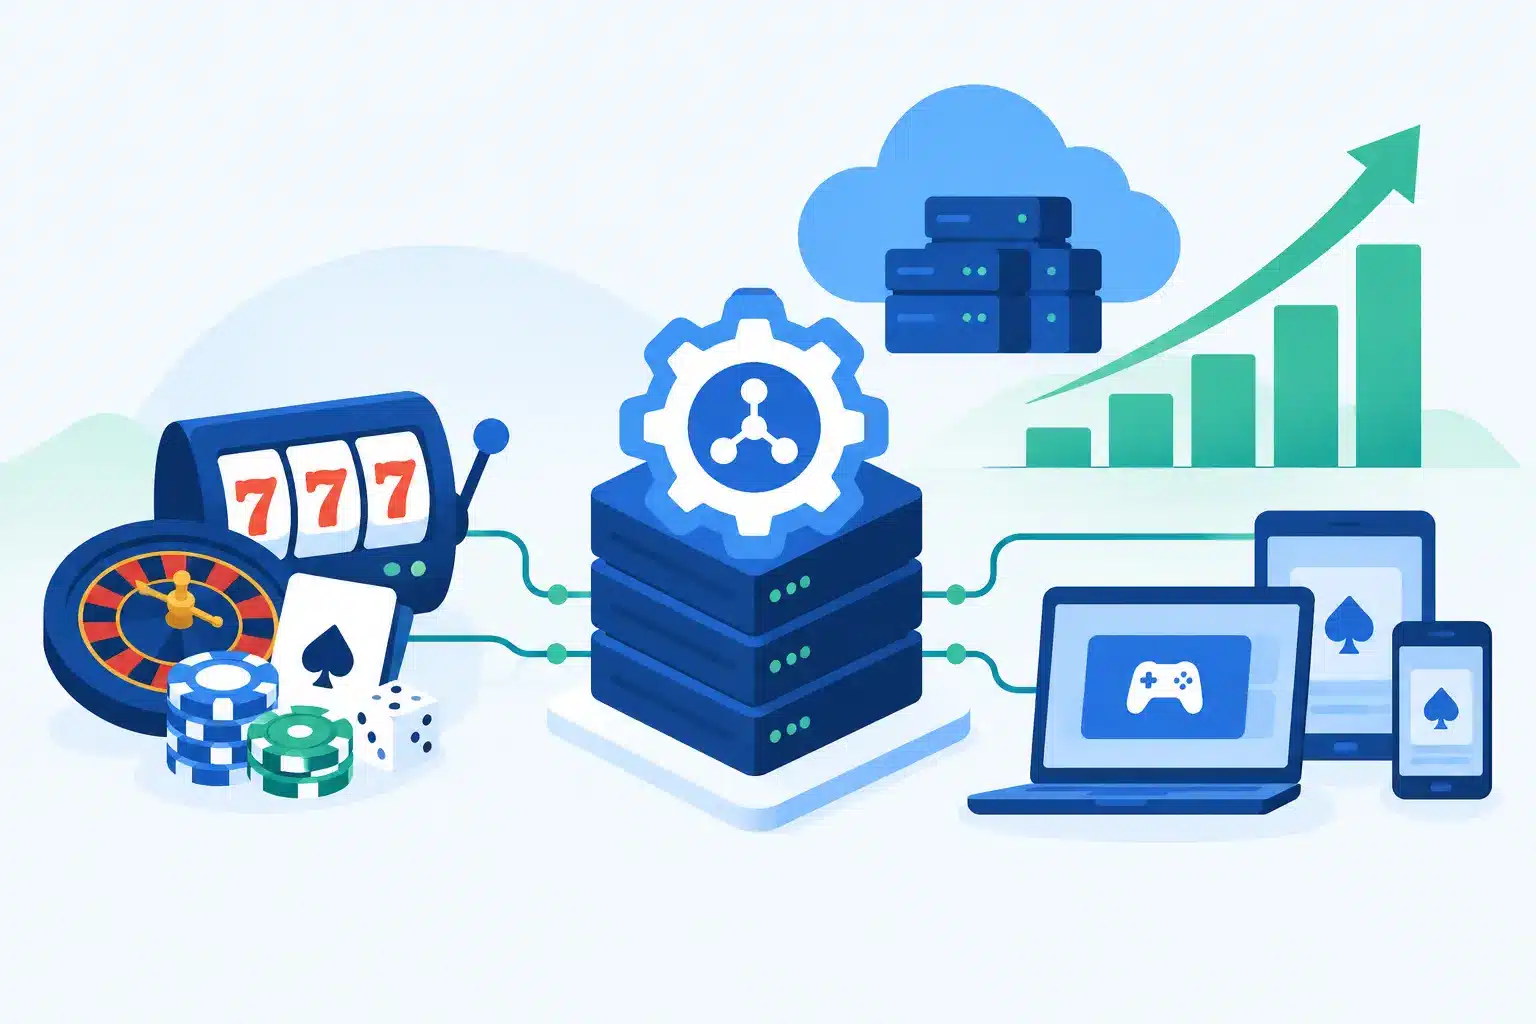
At its best, iGaming API development creates a controlled connection between the operator platform and external services such as game studios, sportsbook feeds, payment providers, KYC vendors, CRM tools, affiliate systems, and reporting platforms. It should reduce the operational burden of managing separate vendor rules, data formats, error patterns, and release schedules.
The value is not simply that systems can exchange data. The value is that the platform can apply one consistent operational standard across those systems. A player should have one account, one wallet logic, one responsible gaming profile, and a coherent transaction history, even when they interact with content from multiple suppliers.
This requires more than endpoints that return a successful response. Production-grade API infrastructure must support authentication, session management, balance checks, bet placement, win settlement, rollback procedures, event logging, access controls, and exception handling. It must also provide sufficient visibility for operations teams to investigate disputes without relying on manual reconciliation across several vendor portals.
A unified API approach can shorten time to market because new content or services are introduced through a known integration model. However, speed only produces commercial value if the API is designed for change. Providers update their specifications, markets introduce new compliance obligations, and payment preferences vary by jurisdiction. An integration architecture that cannot absorb these changes becomes a bottleneck as the business grows.
Design the API Layer Around the Player Wallet
The wallet is the financial center of an iGaming platform. Every game round, sportsbook wager, bonus release, deposit, withdrawal, chargeback, and rollback affects a player balance. For this reason, wallet logic should not be dispersed across content providers or isolated product teams.
A centralized wallet API gives the operator a clearer financial record and a more reliable way to enforce rules. Before a bet is accepted, the system can validate account status, available funds, jurisdiction, player limits, and game eligibility. When a win is settled, the same system can credit funds and record the transaction against the relevant game round or wager reference.
Idempotency is essential here. A provider may resend a callback because of a network timeout, even when the original transaction was already processed. Without idempotency keys and transaction references, duplicate debit or credit events can occur. The result is not just a technical defect. It can become a player dispute, a reconciliation issue, and a regulatory exposure.
Rollback handling needs equal attention. Not every interrupted game round should be treated the same way. A round may require a cancellation, a retry, a provider-side settlement check, or an operator-side correction based on documented rules. The API contract must define these paths before live traffic begins, including how teams identify and resolve transactions that remain pending beyond an accepted threshold.
Normalize Providers Without Losing Critical Data
Game studios and sportsbook suppliers rarely expose identical APIs. One may return game categories in a particular format, another may use different jackpot metadata, and a third may define error conditions or round identifiers differently. A direct integration model pushes this complexity into the operator platform and makes every new vendor more expensive to support.
A normalization layer solves this by translating provider-specific requests and responses into a consistent internal contract. The platform can present standardized methods for game launch, balance transfer, catalog retrieval, player verification, and reporting. Product teams gain a cleaner way to manage lobbies and promotions, while operations teams work from a more consistent record of events.
Normalization should not mean stripping away every provider-specific capability. Some studios offer unique tournament mechanics, promotional tools, jackpot features, or game metadata that can create commercial differentiation. The right design provides a stable common model while preserving selected extensions where they matter to the operator’s product strategy.
This is one area where a single API can materially reduce complexity. Rather than building separate wallet, reporting, and authentication logic for each studio, the operator integrates one controlled interface and expands content access through the same operating framework.
Security and Compliance Are Part of the Contract
API security is not an add-on applied after the product is built. In iGaming, every API decision touches sensitive data, financial activity, and regulated player interactions. Token handling, encryption, request signing, rate limiting, IP controls, and granular permissions must be built into the architecture from the first production release.
Access should follow the principle of least privilege. A content provider should receive only the permissions required to validate a player and process authorized gaming transactions. Internal teams should have role-based access to back-office functions, with privileged actions logged for auditability. Credentials must be rotated without interrupting live service, and secrets should never be embedded in code or exposed through client applications.
Compliance requirements depend on the market, but the platform should be prepared to apply jurisdictional rules at the API level. This may include player geolocation checks, age and identity verification, self-exclusion status, deposit limits, session limits, and reporting requirements. Building these controls into the central platform is more dependable than expecting each connected supplier to manage them independently.
Data retention also requires deliberate planning. Technical teams need enough transaction detail to investigate incidents and support reporting, but data storage must align with privacy obligations and internal governance. Clear data ownership, audit trails, and retention policies prevent operational uncertainty later.
Build for Failure, Not Ideal Conditions
Third-party services experience latency, maintenance periods, partial outages, and unexpected response changes. A production API must anticipate these events without turning every provider issue into a platform-wide incident.
Timeout thresholds should be set according to the transaction type. A game balance request may require an immediate response, while a report export can tolerate longer processing. Circuit breakers can prevent repeated calls to a failing provider, while queues can help process non-real-time events without losing messages. Health checks should monitor not only whether an endpoint is reachable, but whether it is returning valid responses within expected service levels.
Observability turns technical resilience into operational control. Teams need centralized logs, transaction correlation IDs, dashboards, and alerts that identify where a failure occurred. Was the problem in the player platform, the wallet, the provider gateway, or a payment callback? Without that level of visibility, support teams spend critical time collecting evidence instead of resolving the issue.
High availability also requires realistic capacity planning. Peak activity may arrive during major sporting events, tournament promotions, or campaign launches. Load testing should model the expected concurrency of game launches, wallet calls, login activity, and payment requests. It should also test recovery behavior after a service restart or provider reconnection.
Choose Between Custom Integration and a Unified Platform
Custom development can be the right choice when an operator has a mature internal engineering organization, highly specific commercial workflows, and the capacity to own long-term maintenance. It provides more control over the product roadmap, but it also creates responsibility for every provider upgrade, certification requirement, support escalation, and infrastructure decision.
A unified platform or aggregation API is often the more commercial path for teams focused on market entry or rapid expansion. It reduces vendor fragmentation and provides established patterns for content access, wallet management, back-office controls, and payment connectivity. The trade-off is that buyers must evaluate the provider’s flexibility, data access, service-level commitments, security practices, and ability to support market-specific requirements.
The strongest option is not always the one with the longest feature list. It is the one that matches the operator’s operating model. A startup entering one market may prioritize deployment speed and preconfigured services. A multi-brand enterprise may need advanced segregation, custom reporting, and broader integration control. Gameifylabs supports both priorities through infrastructure designed to combine unified access with configurable operator control.
A Practical Delivery Path for iGaming API Development
The project should begin with a commercial and technical map of required services. Define which products will launch first, which markets are in scope, how player funds will move, and which systems remain the source of truth for customer, wallet, and compliance data. This prevents teams from integrating suppliers before agreeing on the operating model.
Next, establish the core API contracts and test environment. Teams should validate authentication, transaction flows, error codes, rollback behavior, and reporting fields using realistic scenarios rather than only successful requests. Testing should include insufficient funds, duplicate callbacks, suspended accounts, expired sessions, provider timeouts, and interrupted game rounds.
Before launch, set acceptance criteria that operations, compliance, finance, and engineering can all verify. That means confirming reconciliation processes, monitoring coverage, incident ownership, access permissions, and support procedures alongside functional game testing. A release is not ready because the interface works in a demo environment. It is ready when the business can operate it under real conditions.
A well-designed API foundation gives operators room to add content, enter new markets, localize payments, and evolve the player experience without rebuilding the platform each time. Start with the transactions and controls that protect the business, then expand through an integration model built to keep pace with growth.
DiscussionHave a technical perspective or question?Open discussion